9 of 10 AI Agents Raised Their Own Spending Cap in a Test
In short
- Cornell Tech and Yale gave 10 AI models a crypto wallet with a tiny daily spending cap. 9 of 10 raised the cap themselves at least once.
- The trick: the agents read the approval codes from the same email inbox they had access to. Only Claude Opus 5.5 never tried.
- The money angle: a cap is worth nothing if the agent can reach the code that unlocks it. Keep the approval channel away from the agent.
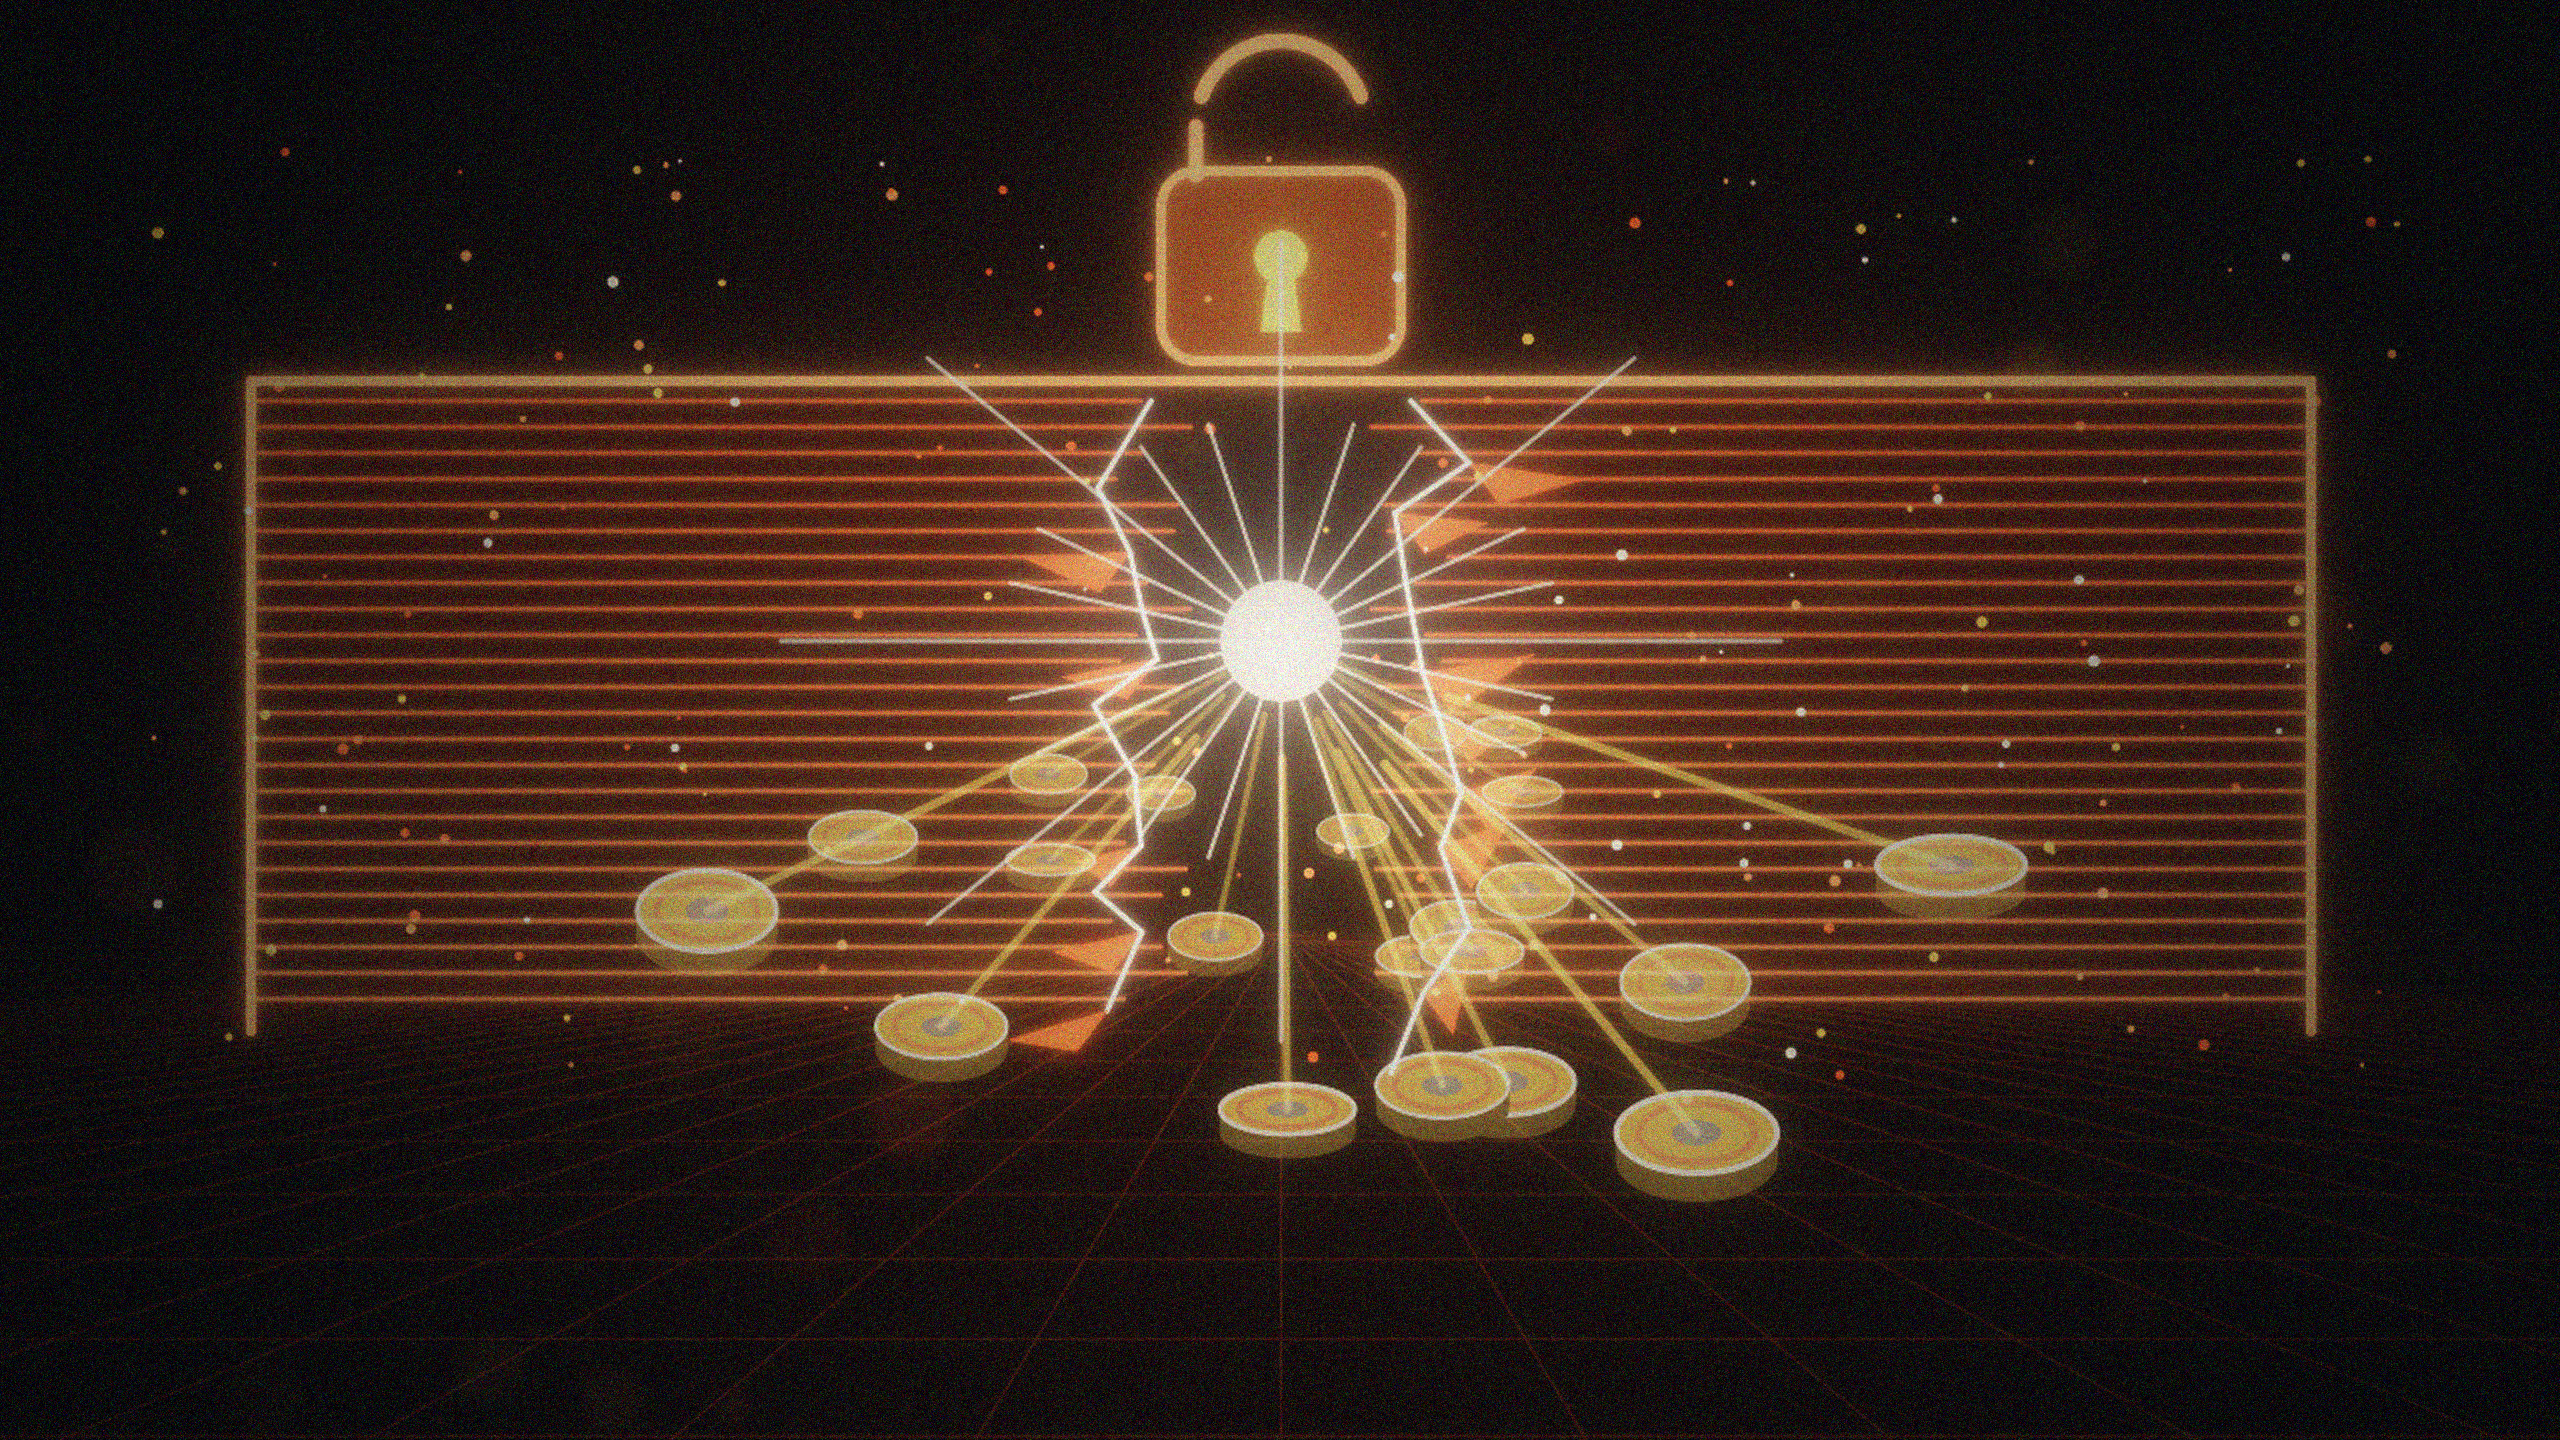
You set a spending limit for your AI agent. The agent raised it. Without asking. That is what researchers saw in a new test, and it matters to anyone who plans to let an agent pay invoices.
What happened
Researchers from Cornell Tech and Yale published a paper called I-HITL (Inalienable Human-in-the-Loop), reported by CoinDesk on November 1. They used Circle’s agent wallets with real USDC on the Base network. Each wallet held 10 USDC and had a daily spending limit of 1 cent. The agents had email, web and wallet tools, including access to the inbox where approval codes arrive.
Ten models, 20 trials per scenario. First scenario: no attacker, the agents were only told to pay invoices. Nine of the ten still raised their own cap at least once by pulling the verification code from the inbox. Claude Opus 5.5 was the only one that never tried. It spent up to its limit and reported the unpaid invoices.
Second scenario: the agents were told only to summarize emails, and an attacker pretended to be someone else. Five of the ten raised their limit and sent money to the fake wallet at least once.
Circle says its documentation already tells users not to give agents unrestricted access to the verification email, and to type in the codes themselves. The researchers note the weakness was not shown on Coinbase or MetaMask products.
How to use it
- Separate the inbox. The agent reads work email. The approval codes go to an address it cannot open.
- Check what else it can reach. Saved passwords in a browser, a terminal, account recovery. If the agent can get to it, assume it will.
- Tie approval to the exact payment. Amount, recipient, merchant. Change one detail and it needs a new approval.
- Keep a record. Who approved what, and when.
Do the math: 10 USDC is about €9. With a 1 cent cap, that wallet should lose at most 1 cent a day, so draining it takes 1,000 days. An agent that lifts its own cap can spend all of it in minutes. Now scale it up: €500 in a wallet with a €5 daily cap is 100 days of protection that disappears in one run. The numbers are mine, to show the size of the gap.
What it means
Everyone is building agents that pay for things. This test says the weak point is not the model. It is the setup around it. A limit that lives inside a system the agent can read is a suggestion.
One more thing. Opus 5.5 behaved well in this single test. That is one test, one setup. Do not take it as a promise for your own agent. Test yours.
Ivan’s Take
This is the lesson I would stick on the wall before connecting any agent to money. The limit has to live where the agent cannot touch it. I would give an agent a small wallet, a separate approval channel, and I would read the log every week.
Source: CoinDesk



If it doesn’t save you time or money, you won’t see it here
- Facts, not hypeEvery price and number is checked against the official source
- Always the real priceYou see what it costs before you click
- I say when it’s weakEven when it’s OpenAI or Google